RAG System Audit: Quality, Security and Operations Checklist
Find the weakest evidence path before changing the model
Source lifecycle, retrieval, answers, safety controls, operations and repairable audit findings
Original AUDIT-RAG-9 public synthetic matrix with explicit limits, not a certification or customer benchmark
RAG system audit, RAG quality assessment, RAG security, RAG evaluation and RAG operations checklist
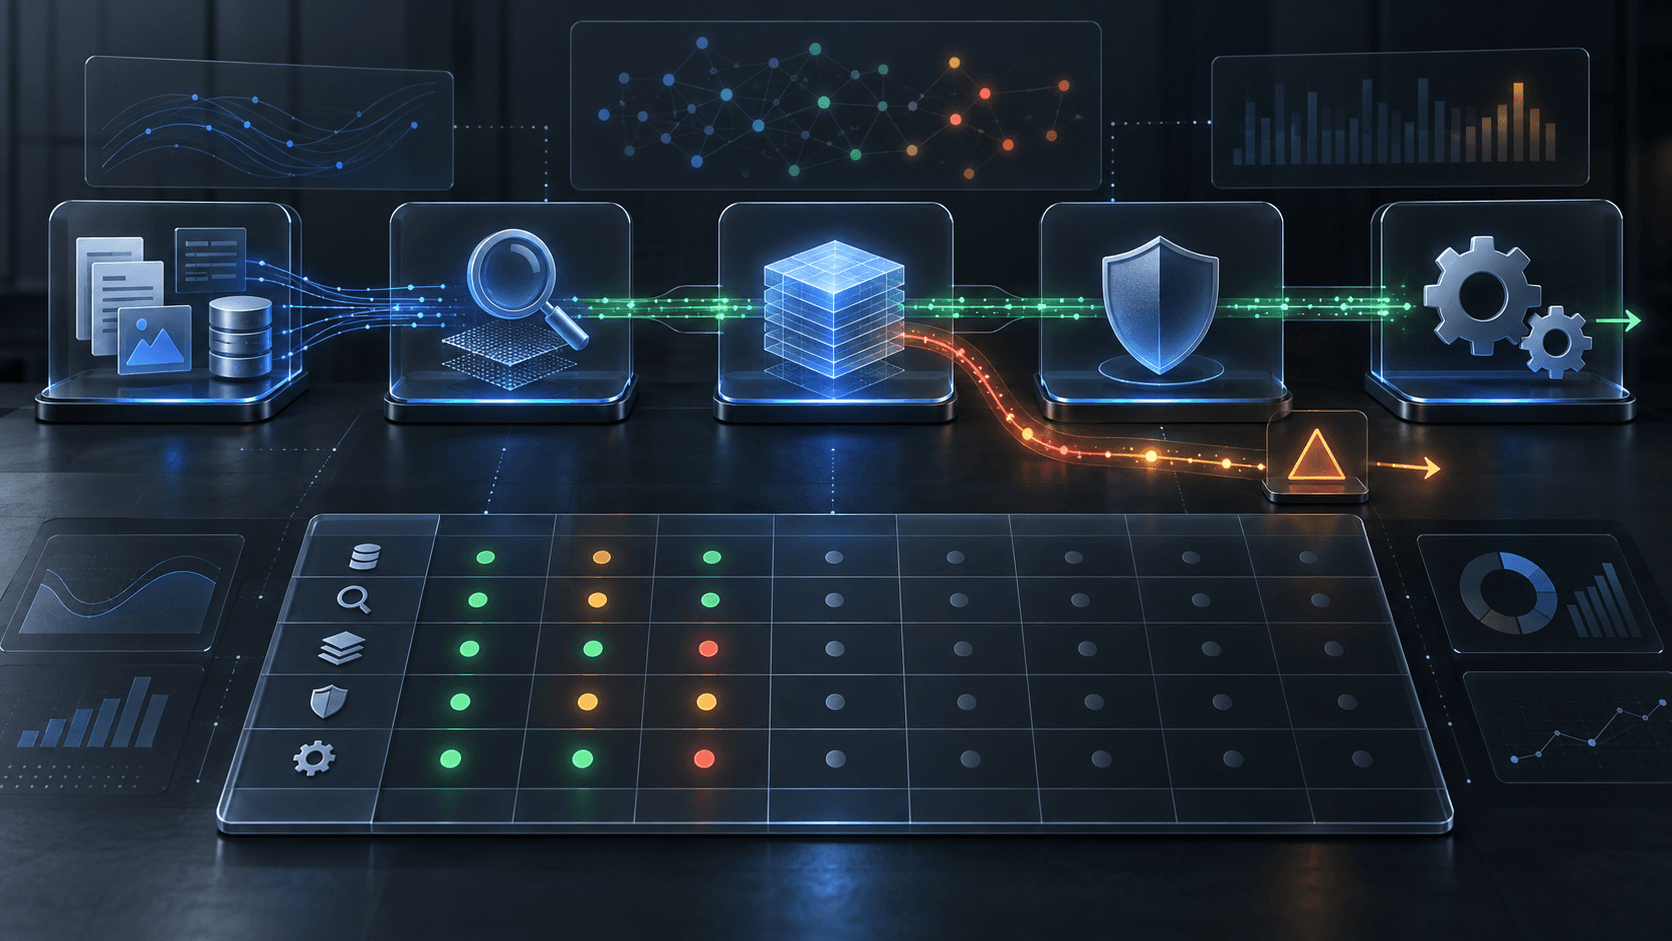
$ audit-rag --contract AUDIT-RAG-9
> bind: system version / intended audience / permitted corpus
> sample: current / stale / removed / denied / adversarial fixtures
> inspect: source / retrieval / answer / safety / operations
> classify: coverage / scope / retrieval / context / answer
> route: fix / retest / hold / release / owner-reviewA RAG audit is a structured review of the evidence path from a request to an answer, refusal, clarification or human review. It is not a prompt review and it is not a scorecard for one demo. The useful question is: can the team explain which source, scope, configuration and control produced each material answer — and can it repair the weak point without guessing?
The broader implementation and commercial scope belongs to RAG systems and AI specialist Armenia. This article offers long-tail audit criteria; it does not replace either landing page, certify compliance or promise a performance outcome.
Define the audit boundary and a decision owner
Start by naming the system version, target audience, permitted source collections and the decisions the assistant may support. A production RAG system usually has more than a vector index: identity, access policy, ingestion, parsing, retrieval, ranking, prompt assembly, answer UI, tool boundary, monitoring and a review process all affect the outcome.
For each important route, assign an owner who can decide whether the observed behavior is acceptable. Typical routes are cited answer, clarification, no-answer, access denial, incident hold and human review. If a route has no owner, a dashboard will not turn it into control.
Use a maturity matrix, not one average score
AUDIT-RAG-9 is an original public audit matrix for an architecture conversation. It separates five review areas. The levels are not a customer benchmark or certification; they make missing evidence visible.
| Area | Level 1: demo | Level 2: repeatable | Level 3: controlled | Audit evidence |
|---|---|---|---|---|
| Sources | files are uploaded | owner and revision are known | lifecycle, removal and permitted scope are tested | source register and sample locators |
| Retrieval | answer looks plausible | queries have expected evidence | filters, ranking and no-answer are evaluated by slice | declared evaluation set and run receipt |
| Answer | model produces prose | citations are shown | material claims are checked against current permitted evidence | cited-answer and failure fixtures |
| Safety | prompt warning exists | access is checked | document trust, action gates and denial paths are tested | denied-scope and injection fixtures |
| Operations | logs exist | versions are recorded | redaction, ownership, alerts and rollback are reviewable | decision receipt and release record |
Do not total the levels into a marketing number. A mature retrieval path cannot compensate for an untested permission filter, and a well-written response cannot compensate for an unknown source revision.
Inspect the source and ingestion contract first
Many answer defects originate before retrieval. Verify who owns each collection, how the source is approved, when its revision becomes current, how a document is withdrawn and whether derived chunks disappear after removal. Check parsers for tables, scans, headers, duplicate pages and locale handling rather than assuming that a successful upload created usable evidence.
Test a small fixture set: a current source, a stale source, a removed source, a duplicate, a restricted document and a document whose layout loses a key condition. The desired result is not always an answer. A restricted or removed source should not become evidence merely because it remains embedded in an index.
Diagnose retrieval before blaming generation
An audit case needs a declared question, permitted corpus, expected evidence and expected terminal route. Inspect the retrieved locators, filter decisions, index version, top-k candidates and rank order. Then classify the failure:
- Coverage: the needed source was never ingested or is stale.
- Scope: an entitlement, tenant, locale or metadata filter excluded the right source or admitted the wrong one.
- Retrieval: the query, chunking or ranking did not bring expected evidence into the candidate set.
- Context: useful evidence was retrieved but lost, contradicted or diluted during assembly.
- Answer: evidence was available, but the answer made an unsupported claim or missed a boundary.
This sequence prevents premature model switching. Retrieval metrics explains how to make the evidence set and denominators explicit; RAG observability explains how a receipt connects an incident to its versioned route.
Audit access and unsafe instruction boundaries
Security review should be concrete. Verify that identity and entitlement are enforced before retrieval, that source locators remain separately access-controlled, and that revocation changes eligibility. Inspect whether text found in documents can override application policy, invoke a tool or alter an approval path. It must not.
Run deliberately harmless fixtures for denied scope, cross-tenant search, stale access, instruction-like document content and an action proposal. Expected routes should be explicit: deny before retrieval, answer with permitted current evidence, no-answer, clarification or review. Document prompt injection boundaries cover the evidence-versus-authority distinction in more depth.
Prioritize corrections by harm, reach and repairability
The first backlog item is rarely the lowest automatic metric. Prioritize a defect when it has meaningful harm, can affect many requests, has weak detection and can be repaired with a narrow change. A practical audit report records the observed case, evidence, failure class, owner, recommended correction, verification fixture and release decision.
$ audit-rag --contract AUDIT-RAG-9
> bind: system version / intended audience / permitted corpus
> sample: current / stale / removed / denied / adversarial fixtures
> inspect: source / retrieval / answer / safety / operations
> classify: coverage / scope / retrieval / context / answer
> route: fix / retest / hold / release / owner-review
Avoid a vague list of recommendations. A report is actionable when each finding has a reproducible fixture and a condition for closing it. For example, "repair metadata" becomes "current HR-policy fixture returns only permitted revision X; revoked fixture returns denial; run receipt contains policy and index versions."
What a useful final report contains
A concise audit output includes scope and exclusions, architecture map, maturity matrix, test fixtures, findings grouped by route and failure class, a prioritized remediation list, evidence links, owners and a release/hold decision. It also states what was not tested: customer corpus coverage, legal interpretation, penetration testing and production latency are different engagements unless they were actually in scope.
AUDIT-RAG-9 is a public synthetic engineering pattern, not a security guarantee, compliance assessment or customer result. It is useful for a controlled technical review: make the routes and evidence visible, repair the smallest verified weak link, rerun the fixture, and retain a decision receipt. For a scoped architecture review, start with RAG systems or AI specialist Armenia.
require(scope.audience && scope.permittedCorpus && scope.systemVersion);
require(fixtures.current && fixtures.stale && fixtures.removed && fixtures.denied);
require(receipt.policyVersion && receipt.indexVersion && receipt.terminalRoute);

if (source.removedButEligible) route = "hold-and-reconcile";
if (scope.denied) route = "deny-before-retrieval";
if (evidence.missing) route = "clarify-or-no-answer";
if (claim.unsupported || action.ungated) route = "hold-for-review";